

Elevate Your Clients’ Security Posture with IBM Security QRadar SIEM
Digital transformation applications and cloud-based data are attractive targets for bad actors. But, alarmingly, security operations technologies and legacy platforms may struggle to deal with these threats.
This is why SOC modernisation is high priority for security teams as organisations integrate technologies, adopt new types of analytics solutions, and automate SOC processes.
IBM Security QRadar SIEM is a solution laser-focused on improving an organisations security posture, and when it is partnered with NDR it helps deliver a broader XDR strategy.
With over 700 integrations, 1,500 out-of-the-box use cases and built-in network visibility IBM Security QRadar SIEM has the power to analyse every aspect of your environment, find suspicious activity and facilitate rapid responses. IBM QRadar has the agility to detect threat actors when they trigger multiple detection analytics, move across the network or change their behaviours. It tracks each tactic and technique used throughout a kill chain, scores the offense, and automatically prioritizes high-fidelity alerts in real time.
SIEM and NDR: Better Together
This white paper from Jon Oltsik, ESG Senior Principal Analyst and Fellow, takes a deep dive into the many challenges facing security operations teams and surfaces with several considered suggestions about SOC Modernisation.
Additional Resources
IBM Security QRadar SIEM datasheet
A concise datasheet that summarizes the main benefits of QRadar, quickly and easily.
6 Myths of SIEM
Do you think SIEM solutions are unwieldy and complex, and therefore only for large organisations? Or do you think a SIEM doesn’t detect unknown threats? This fascinating eBook tackle’s the top six myths about SIEM and investigates what you should expect from a SIEM today.
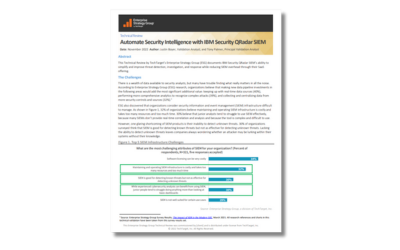
Automate Security Intelligence with IBM Security QRadar SIEM
This technical review outlines IBM Security QRadar SIEM’s ability to simplify and improve threat detection, investigation, and response while reducing SIEM overhead through its SaaS offering. Review why they believe anyone looking to optimise SOC resources without a large investment in SIEM infrastructure should consider QRadar SIEM.
Get in touch
To capture the full value of IBM Security QRadar SIEM for your customers work with Arrow to integrate the IBM security solution into your portfolio and become a go-to provider for cybersecurity solutions.
By completing this form, you agree to the use of your personal information in accordance with the Arrow Electronics Privacy Policy and Terms of Use.
Connect
 |
 |
 |
© 2023 Arrow Electronics, Inc. All rights reserved.